Enabled agent
Owner: Business team
Authorized for: View catalog
RegisteredCONTROL FOR AI AGENTS
Designed to stop AI agents that try to act without identifying themselves or proving authorization.
SIGMA ATG Enterprise is designed to ask every agent to identify itself and prove what it is allowed to do before it reads data, changes records, or uses tools. If it cannot prove its identity or authorization, the operation stops. Sensitive actions can wait for a person to approve them.
THE PROBLEM
A person may sign in to work, but their session does not automatically let any agent read, change, or send everything they can access. Delegation must be specific and verifiable.
Each agent must present a verifiable identity and be recognized locally. The planned console distinguishes internal, external, and unknown agents and associates them with a responsible owner. A valid signature alone does not grant access.
The control compares the requested operation with the permission granted: resource, action, and limits. Permission to view a catalog does not allow price changes; permission to read a record does not allow export.
HOW IT WORKS
An external agent asks to view a record. The request states who the agent is, what it wants to do and which information it seeks.
The system checks whether the organization recognizes the agent and whether it has current permission to view that record.
The request reaches the system only if it meets the rules. A sensitive action may wait for a person to approve it.
CAPABILITIES
The organization defines which agents it recognizes, who is responsible for them, and when they may act.
Permission can be limited to a specific task, resource, and period. It is not open access to the whole system.
A sensitive action can wait for a person’s approval before it continues.
Requests are checked before they reach the application or tool that would make the change.
The design records which agent asked to act, what was decided, and why, so each case can be reviewed.
Planned console for operations, permissions, decisions, and alerts with clear reasons.
REFERENCE ARCHITECTURE
SIGMA ATG Enterprise sits on the route taken by requests to an organization’s portal, application, or tool. Before the system receives an instruction, the control point checks which agent sent it, whether the organization recognizes that agent, and whether this specific operation is authorized. A permitted read can continue, while an unauthorized change is stopped or held for human approval when the rules require it.
The proposal builds on the systems the organization already uses and defines where control belongs for each case. It also covers internal agents using tools managed by the company. A controlled trial checks connections, owners, limits, and the absence of alternate routes to the application. This validation is needed before claiming protection of a real enterprise environment.
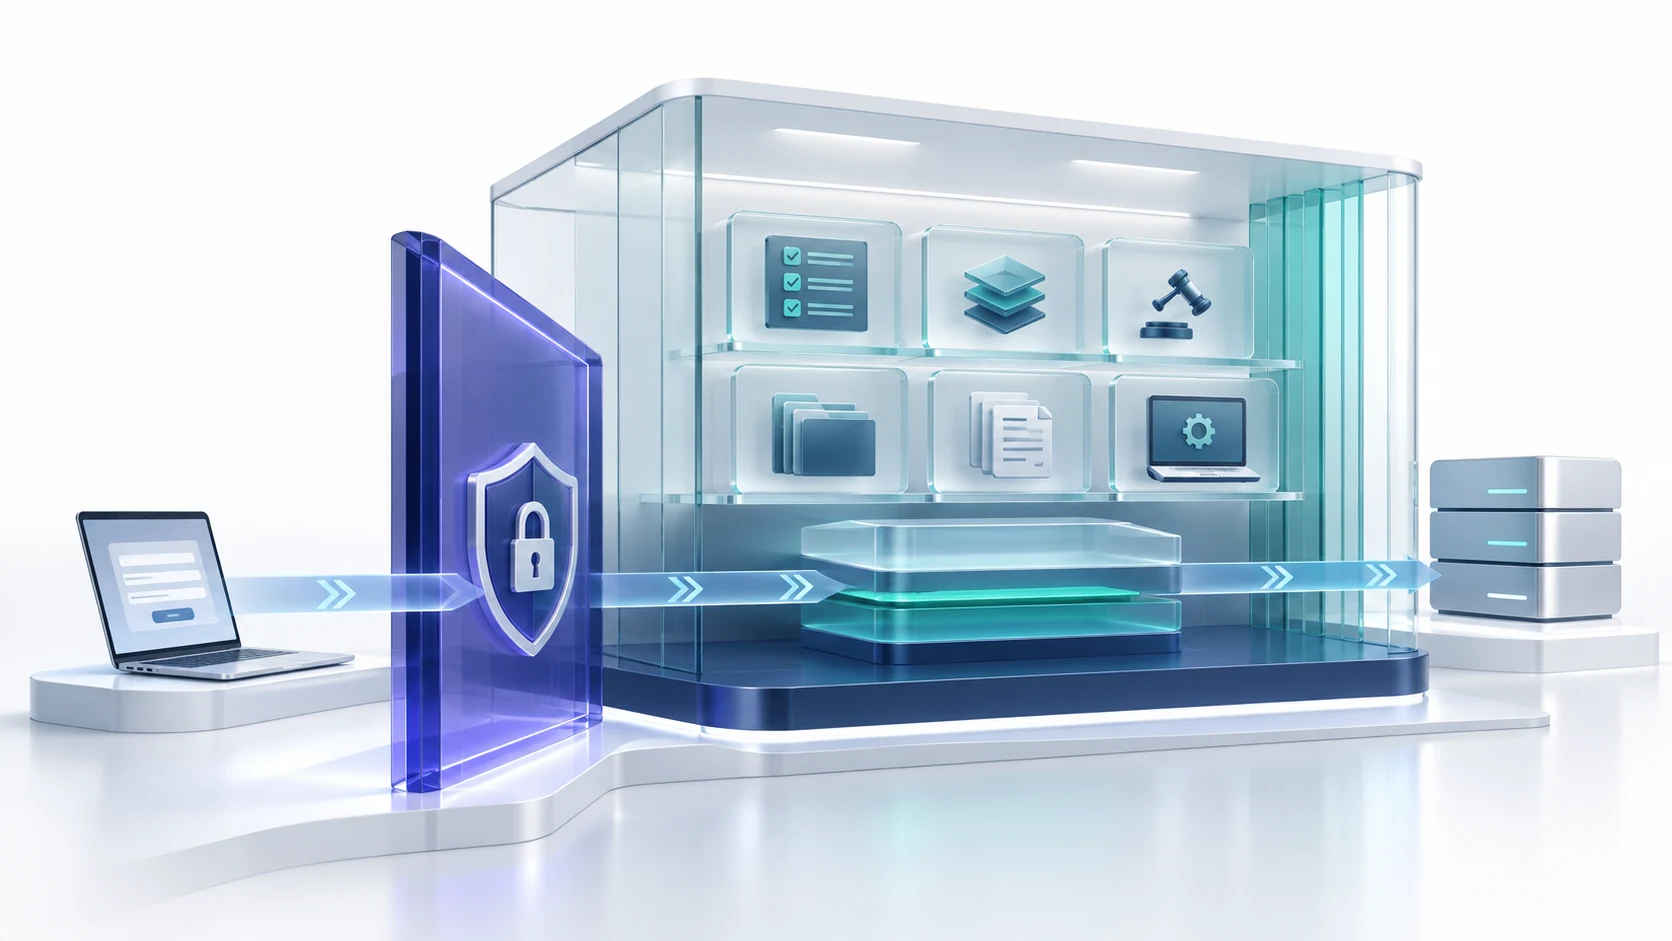
For effective control, there must be no alternate route that lets an agent reach the application directly.
DEPLOYMENT MODES
Protects access to your portals and services: each agent action passes the control point before reaching the system.
Reviews what internal agents do when they use tools and connections the organization controls.
Proposes supervised access to older systems. Protection depends on there being no direct route around the control.
Covers private or restricted settings, subject to specific infrastructure and operational tests.
POSSIBLE APPLICATIONS
Examples of possible uses. These are not customers or existing deployments.
An agent reads business data or prepares changes in internal systems with permission for each task.
Portal and casework tasks with an institutional owner and traceability.
Bounded access to sensitive information by purpose and required approval.
Orders and operational support with system separation and allowed actions.
Automation on digital assets with stronger controls for sensitive changes.
Agents querying inventory or coordinating flows with defined scope and receipts.
External agents read or change business services only within their authorized scope.
Institutional repositories with access scoped by identity and resource.
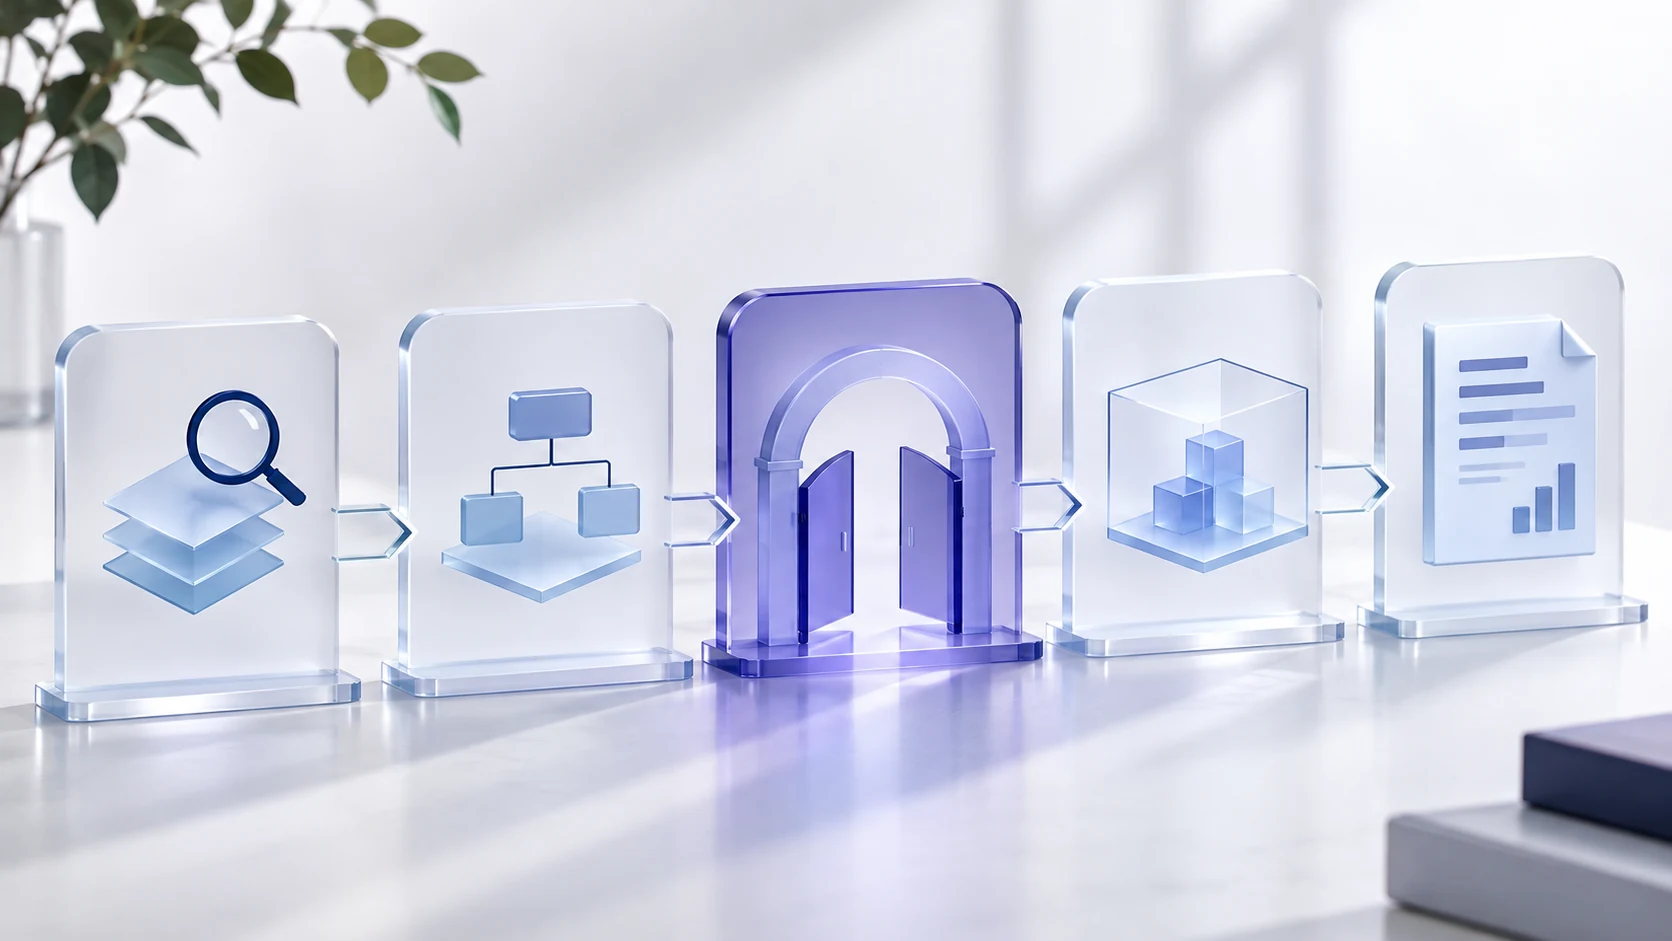
Choose an application, the agents that may use it, and the actions that matter.
Agree on what should be allowed or blocked and how to measure the outcome.
Connect the control to a test environment with a defined scope.
Try to act without permission, exceed limits, or bypass the control point.
Review evidence, limits, and conditions before deciding the next step.
LET'S DISCUSS A POC
Together we select one system, the agents that use it, and a few important operations. We then design a controlled trial to check what is allowed, what is blocked, and what needs approval.